Understand your vulnerabilities is just as vital as risk assessment because vulnerabilities can lead to risks. If there is a universal imperative when it comes to mitigating vulnerabilities, it’s to analyze them first before you try to fix them. The more compound they are, the more critically important this assessment steps becomes.
What is a vulnerability assessment?
A vulnerability assessment refers to the process of defining, identifying, classifying, and then prioritizing all the vulnerabilities that exist in various infrastructures, applications within the company.
With an effective vulnerability assessment, your organization has the tool needed to understand your security weaknesses, how to assess the risks associated with those weaknesses, and last how to put protections in place which reduce the likelihood of occurring.
How to perform a vulnerability assessment
There are three general steps that your company can follow:
- Identify and rang the vulnerability
- Document the vulnerabilities
- Create guidance
Step 1: Identify and rang the vulnerabilities
In this step you should define the risk and critical value for each action. You can construct a matrix with columns for each vulnerability, a possible scenario, the probability of an event and the impact of such an event.
Tip: Focus on what matters most!
Step 2: Document the vulnerabilities
The purpose of the step is to document the vulnerabilities, so you easily can identify and reproduce the findings in the future.
Step 3: Create guidance
Use the profile to provide a clear graphical outline of which actions are associated with the greatest vulnerabilities, and likewise which to consider new or additional measure against.
Tip: Your vulnerability assessment should be reviewed and updated on a regular basis or when changes have been made!
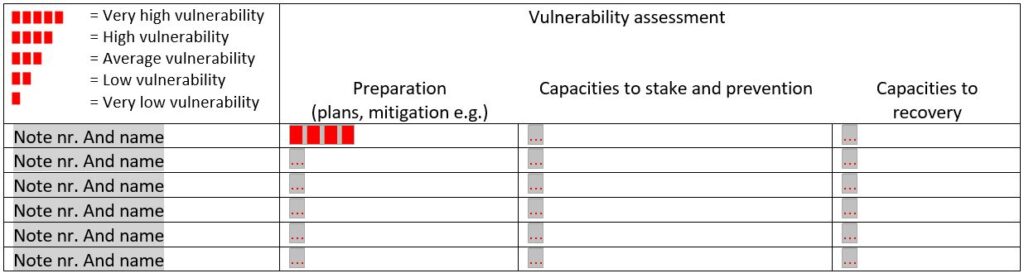
Note: The vulnerability profile cannot stand alone. It should be done along with a risk assessment. (Re)read the post about risk assessment.
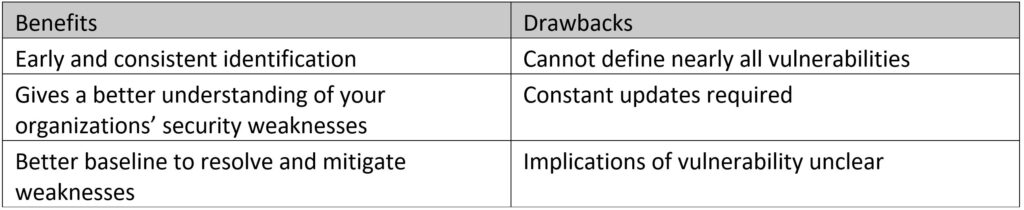
The pros and the cons of vulnerability assessment:
Sources
Snedaker, S. & Rima, C. (2014) ”Risk assessment, Vulnerability Assessment”, in (red.) Business Continuity and Disaster Recovery Planning for IT Professionals, 2.nd. edition
Balbix: “Brief overview of vulnerability assessment”, available online: https://www.balbix.com/insights/vulnerability-assessments-drive-enhanced-security-and-cyber-resilience/